TRUST FAQ

Straight answers to important questions.

Organizations considering ARI should be able to understand how Prairnova approaches security, privacy, AI and customer information without having to decode a technical white paper.

Here are the questions we expect thoughtful buyers to ask.

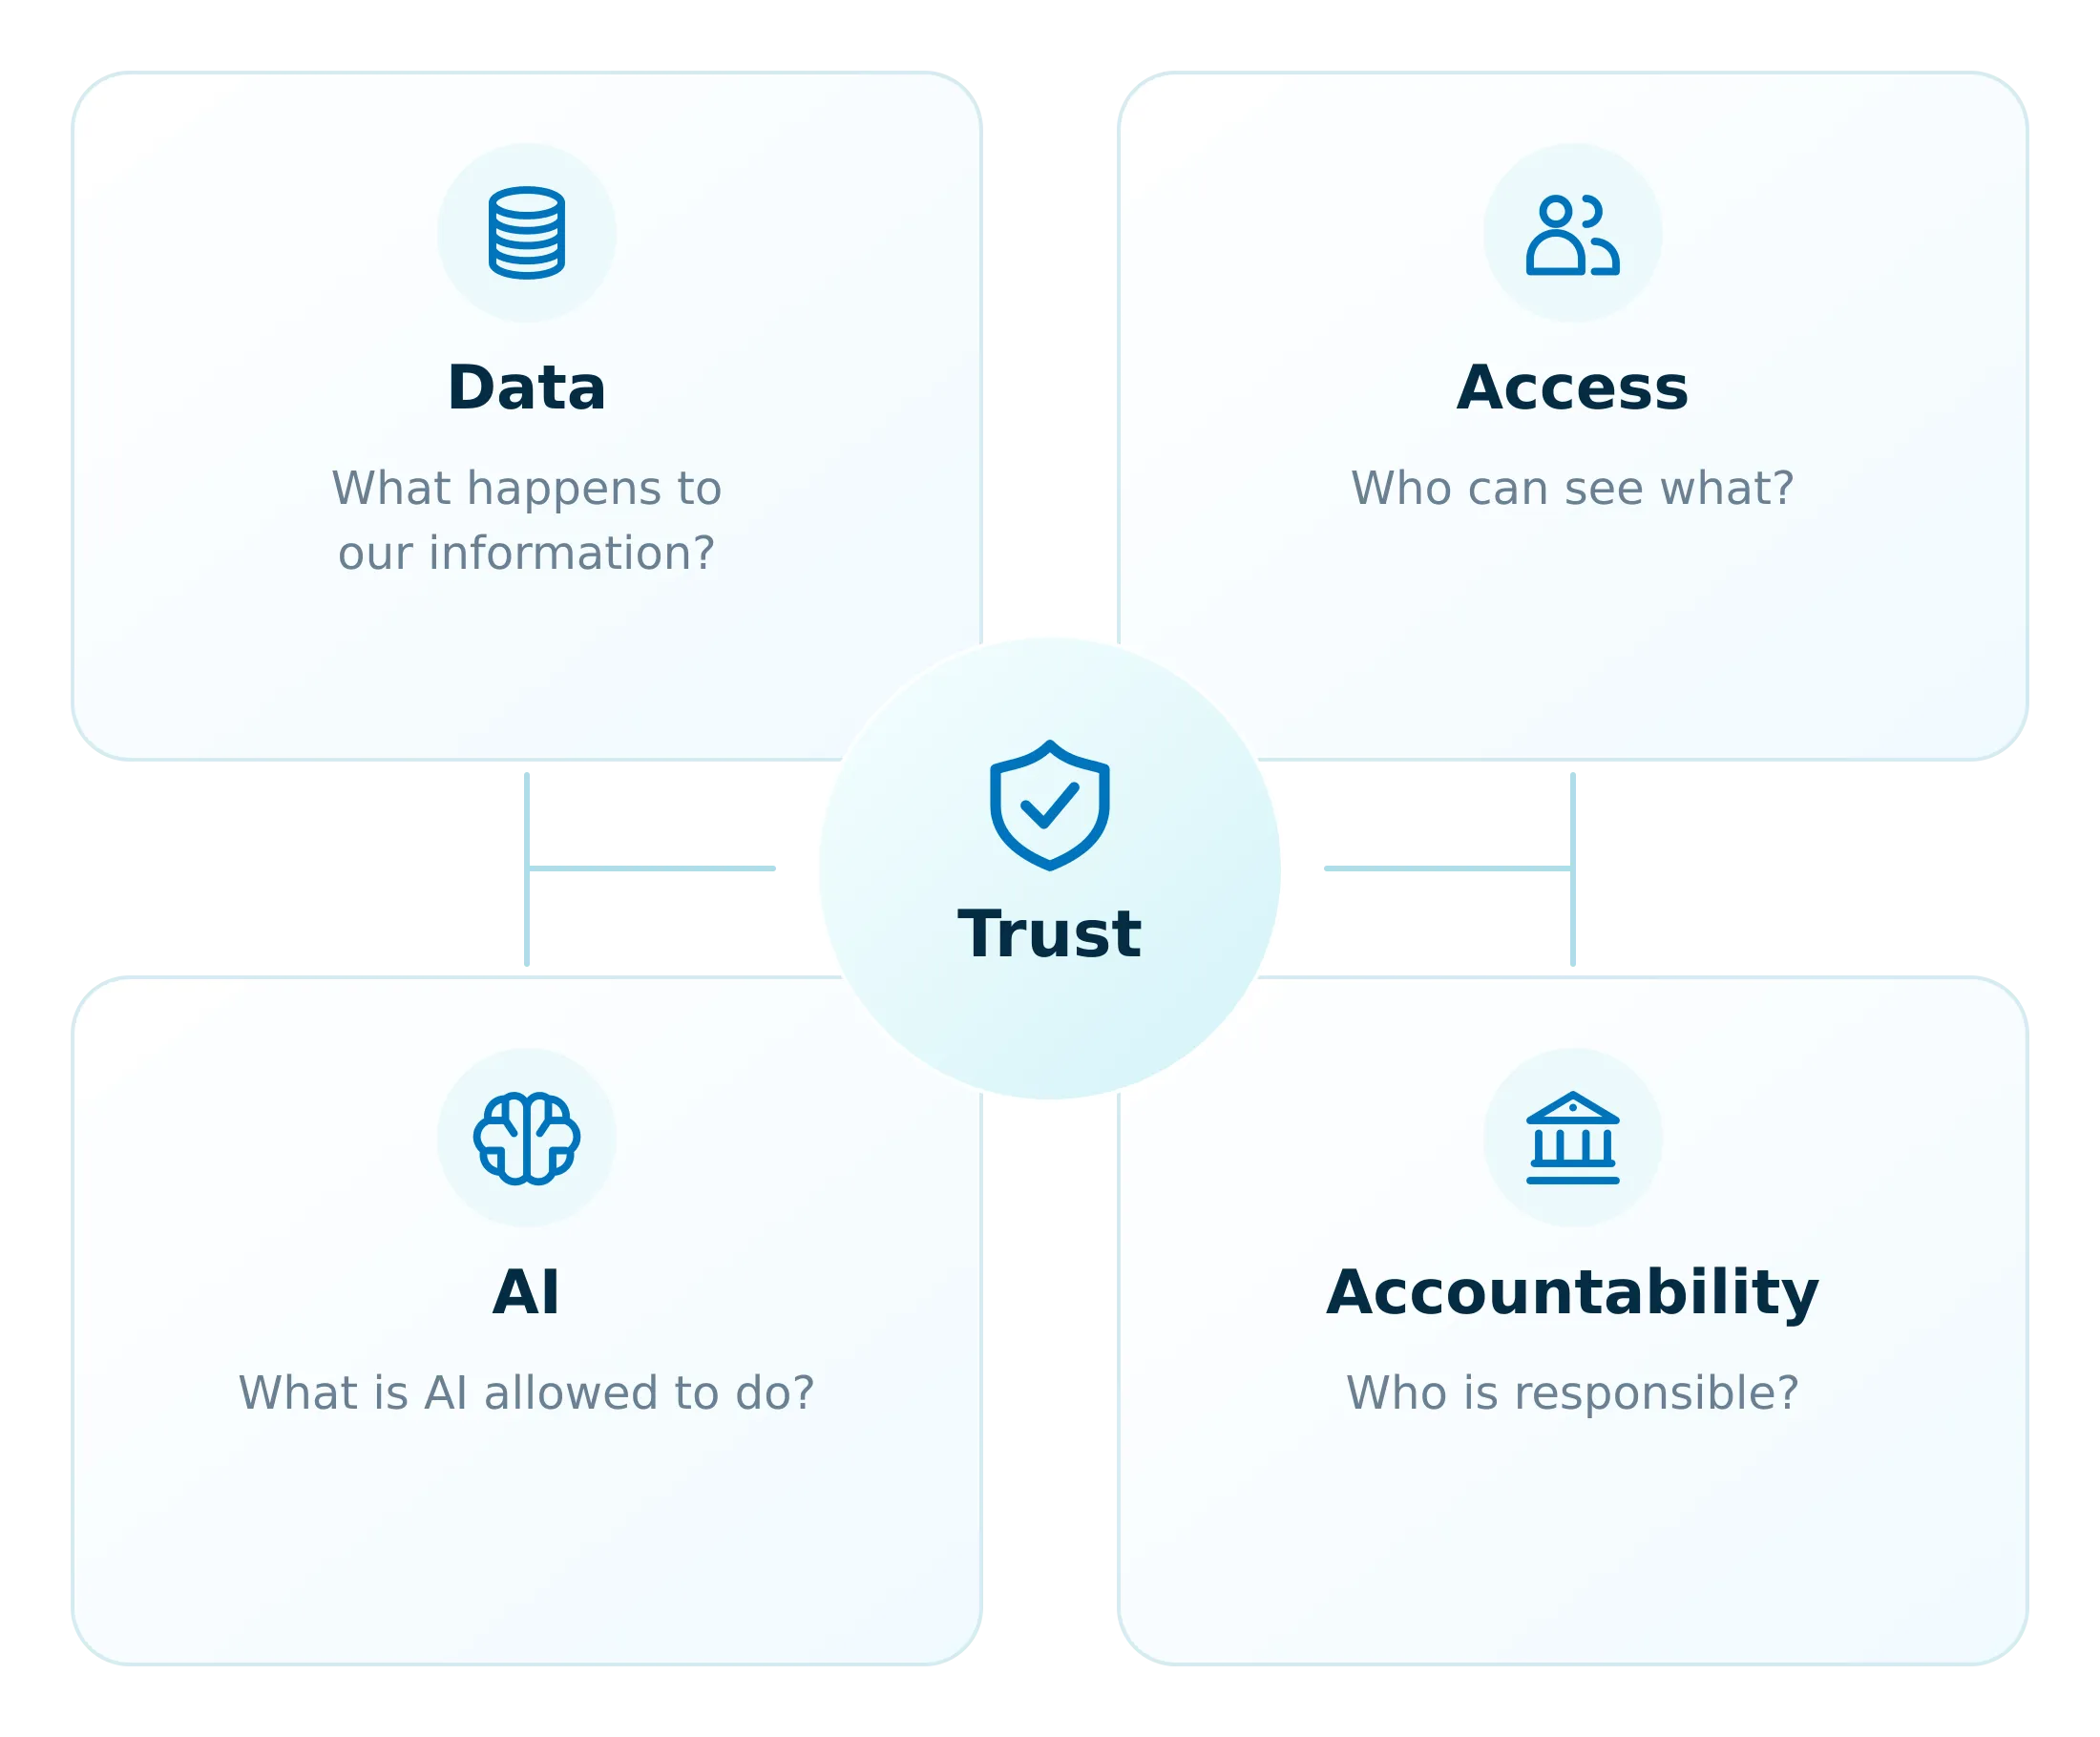
Diagram with a central circle labeled 'Trust' connected to four surrounding squares labeled 'Data: What happens to our information?', 'Access: Who can see what?', 'AI: What is AI allowed to do?', and 'Accountability: Who is responsible?', each with related icons.
01 CUSTOMER INFORMATION

What happens to our data?

Questions about how ARI uses, protects and keeps customer information separate.

Does ARI need access to all of our technology data?

No. ARI is being designed to use the information needed for the intended outcome. The information required depends on the customer environment, product capability and agreed scope.

Learn more in Privacy & Data
Does our information become available to other customers?

It is not intended to. Customer information is designed to remain associated with its organization rather than becoming general knowledge available across other customers.

Does Prairnova use customer information to train a shared AI model?

Not by default. Materially different use would require appropriate governance and customer consideration.

Where will our data be hosted?

Prairnova will document hosting and processing arrangements for the deployed service. We will not make permanent residency or sovereignty claims before verifying the production service.

02 AI & ACCOUNTABILITY

What is AI allowed to do?

Questions about how ARI uses AI, what it can and cannot do, and where people remain responsible.

Does AI make business or risk decisions for us?

No. AI can help organize and explain information; material organizational decisions remain with authorized people.

Can AI grant itself access or permissions?

No. AI output does not create new authority. Access is intended to remain controlled independently of model-generated instructions.

Is AI always right?

No. It can misunderstand context or work from incomplete information. Important outputs should remain open to supporting-evidence review.

03 SECURITY

Who can see what?

Questions about access control, customer boundaries and how ARI and Prairnova handle security.

How is access to ARI controlled?

ARI is being designed around identifiable users, appropriate authentication and least privilege. Exact controls depend on deployment and customer configuration.

Can Prairnova staff access customer information?

Access should be limited to authorized operational or support purposes. Details are covered through controlled security processes.

How are customer environments kept separate?

ARI is being designed around customer boundaries. Detailed isolation architecture and evidence belong in a controlled review.

04 EVIDENCE

Can we see why ARI is telling us something?

Questions about supporting information, explainability and decision context.

Can users inspect information supporting an important output?

That is a core design principle. ARI is being designed so users can review relevant information behind important priorities and conclusions.

Will ARI expose its internal scoring or algorithms?

No. Users should be able to understand why something deserves attention without needing internal algorithms or proprietary product logic.

Does closing an improvement automatically resolve an issue?

No. Completion and demonstrated improvement are not necessarily the same thing. ARI is being designed to review current evidence rather than assume success.

05 INTEGRATIONS

How does ARI fit into our existing environment?

Questions about Microsoft environments, other integrations and required permissions.

Does ARI replace Microsoft Defender, Entra or Intune?

No. Those products continue doing their operational work. ARI is being built to make better use of relevant information.

Is ARI only for Microsoft environments?

No. Microsoft is the initial evidence ecosystem, not the intended boundary of the platform.

What permissions will ARI require?

It depends on the connection and product stage. Connection-specific requirements can be discussed during onboarding or security review.

06 PRODUCT MATURITY

What is available today?

Questions about current capabilities, planned functionality and product maturity.

Is ARI commercially mature today?

ARI is being developed and validated through controlled early-access engagements. Availability and limitations will be described according to their actual stage.

Are all the integrations shown on the website live?

Not necessarily. Connections not ready for customer use will be labelled according to their actual stage.

Is Prairnova SOC 2 or ISO 27001 certified?

Prairnova will not claim certification before it has been achieved. Formal assurance may be pursued as customer demand and maturity justify it.

07 SECURITY REVIEW

Need more detail?

Some questions are best answered in a more detailed conversation.

Blue document icon with a folded top-right corner and three horizontal lines representing text.
We can provide additional information.
For qualified security, privacy or procurement reviews, Prairnova can provide additional technical and assurance information appropriate to the customer requirement, product stage and scope of the engagement.
Talk to Prairnova About Security Review
08 SHARED RESPONSIBILITY

Who owns what?

Security, privacy and resilience are a shared effort.

Icon of a classical building with four pillars and a triangular pediment.
Prairnova
Responsible for the security and operation of ARI within Prairnova’s product and service scope.
Blue icon of two user profiles side by side, representing multiple users or a group.
Customer
Responsible for its users, source systems, internal approvals, business decisions and organizational risk ownership.
Blue shield outline with a checkmark inside representing security or protection.
Together
Both parties have a role in maintaining appropriate access, useful information and effective response when an issue crosses organizational boundaries.

Trust is easier when the conversation is specific.

If your organization has a security, privacy, AI, residency or procurement requirement that is not answered here, talk to us. We would rather address the actual requirement than make a broad claim that may not apply to your environment.

White check mark inside a white circle.
Clear answers
White check mark inside a white circle.
Practical discussions
White check mark inside a white circle.
Appropriate confidentiality
White check mark inside a white circle.
Aligned with your requirements